

The training focused on the examination of digital evidence on the Windows operating system, memory analysis, or RAM Analysis, and the proper process of collecting digital evidence in accordance with computer forensic principles.
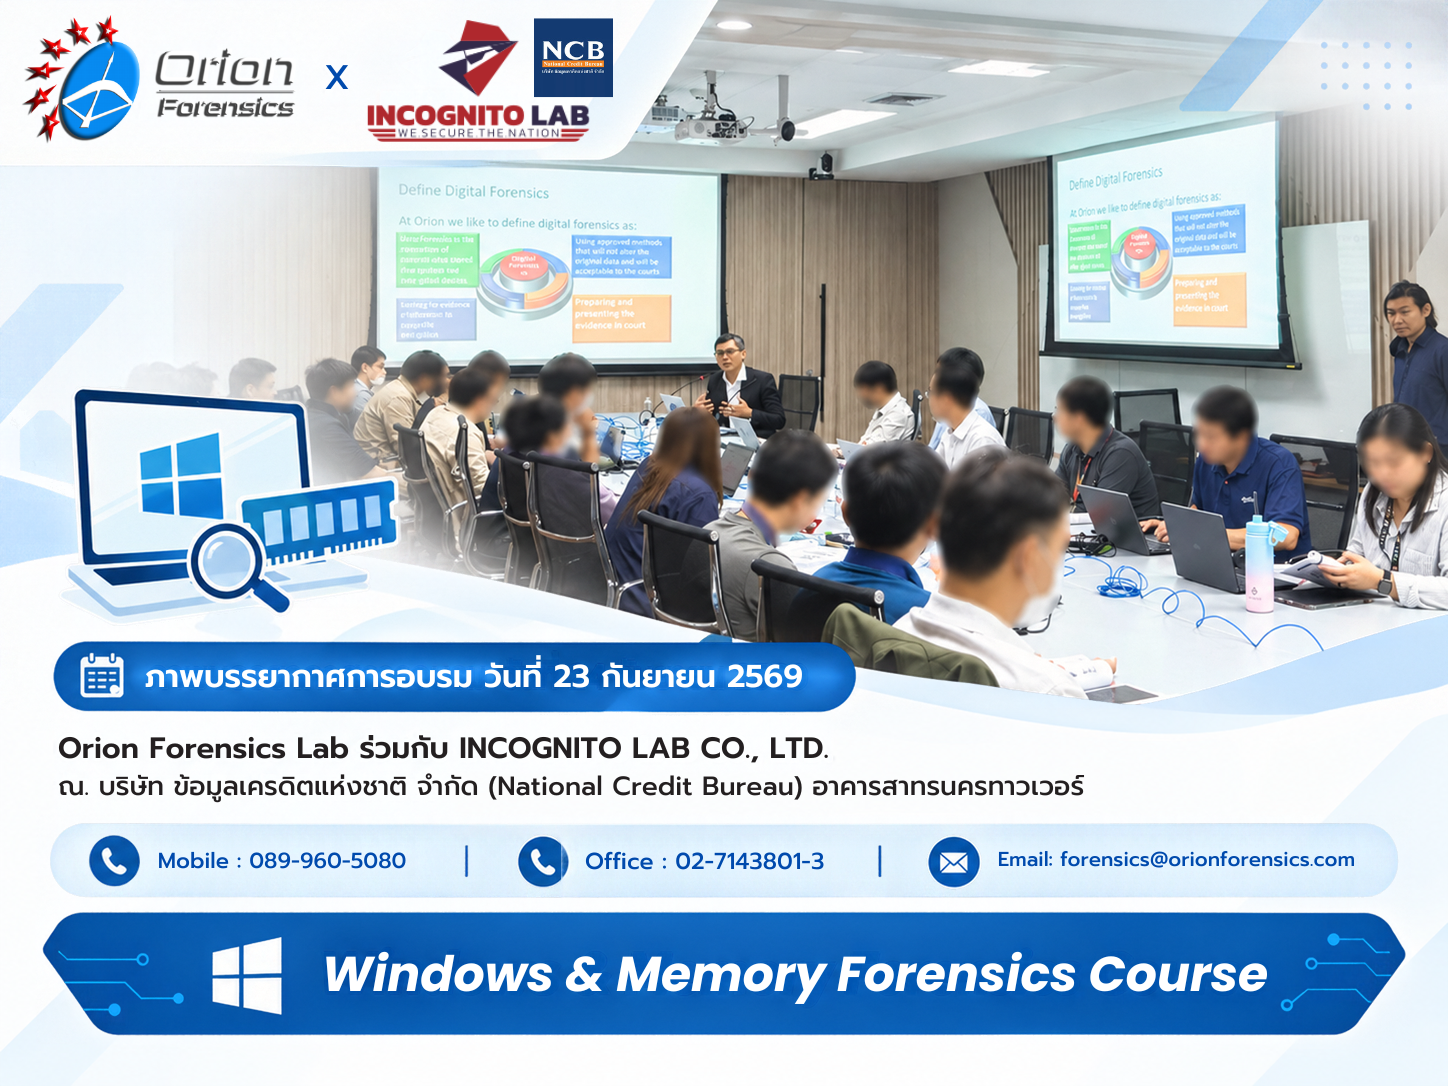
Windows & Memory Forensics Course Training Highlights 23/09/2026
Training Highlights: Windows & Memory Forensics Course

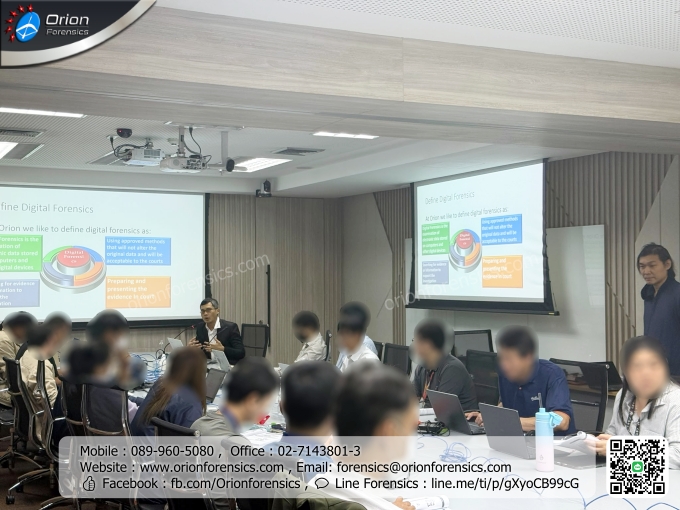
Training highlights from the Windows & Memory Forensics Course
Learning Digital Forensics Through Theory and Practice
Throughout the training, participants learned both the theoretical and practical aspects of Digital Forensics, focusing on the proper collection, preservation, and examination of digital evidence in accordance with computer forensic principles.
The content also covered Memory Forensics techniques used to examine data from system memory to support cybersecurity incident investigations, Malware examination, and Ransomware incident analysis.
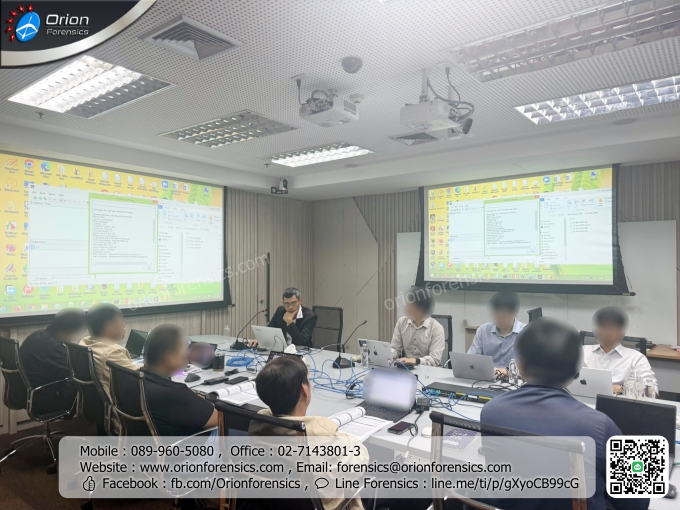
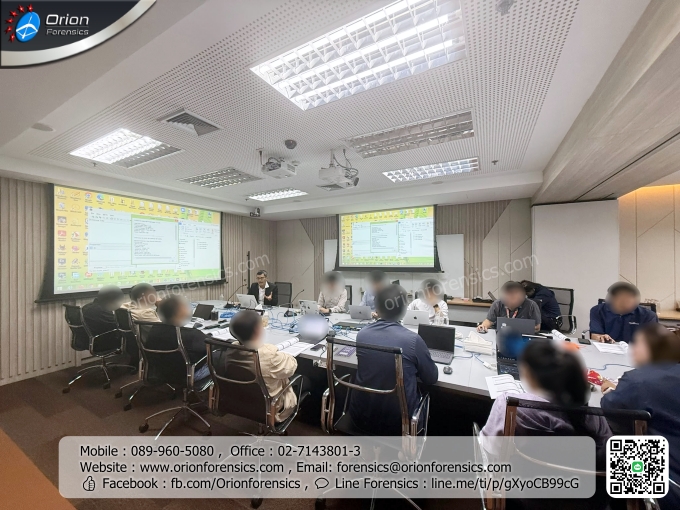
Key Topics in the Windows and Memory Forensics Training
- Forensic Acquisition: The proper collection of evidence from computers while preserving the condition of the evidence
- Windows Artifacts: The analysis of usage traces and important data on the Windows operating system
- Digital Forensic Reports: Examples of digital evidence collection and examination reports
- Memory Forensics: Principles of memory analysis and the differences from Hard Drive Forensics
- RAM Acquisition: Techniques for acquiring data from memory
- Memory Artifacts: The analysis of Processes, DLLs, Registry, and important data within memory
- Malware and Ransomware Analysis: Case studies involving the examination of malware and ransomware using data from memory
Morning Session: Digital Evidence Collection
During the morning session, participants observed a demonstration of equipment and procedures for collecting evidence from computers in accordance with proper Digital Forensics practices.
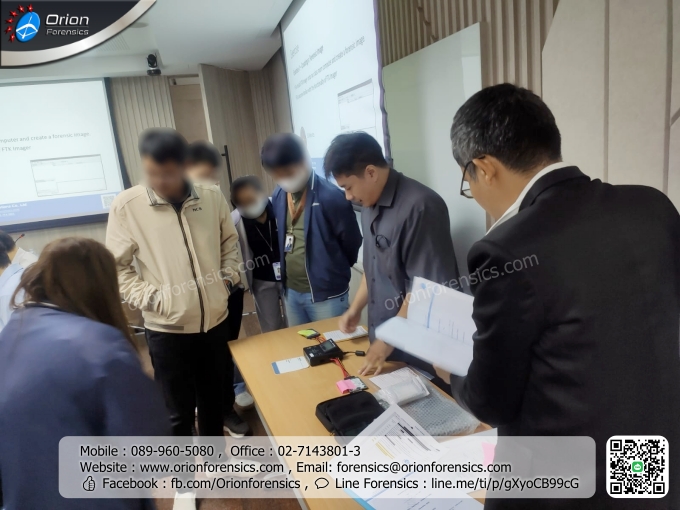
Demonstration of the digital evidence collection and examination process
Afternoon Session: Mobile Forensics and Ransomware Response
During the afternoon session, there was a demonstration of Mobile Forensics tools, along with an exchange of approaches for responding to Ransomware threats and investigating cybersecurity incidents.
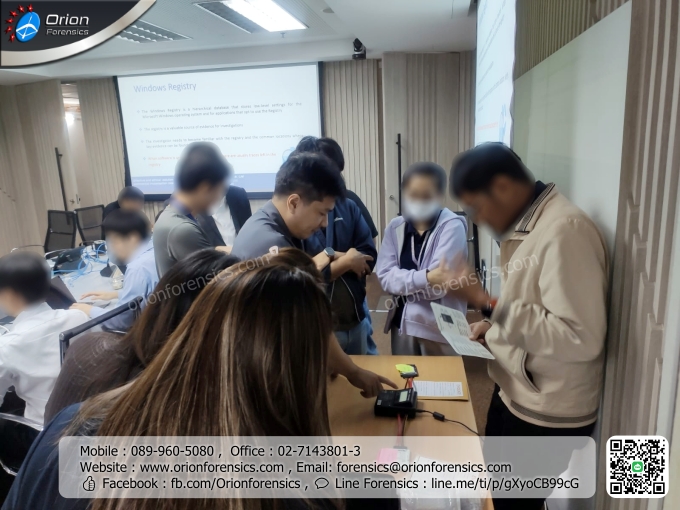
Demonstration of Mobile Forensics tools and cyber incident analysis
Thank You to the Training Participants and Supporting Organizations

This training course was attended by more than 20 participants, who took part in exchanging knowledge, work practices, and different perspectives.
Related Topics: Windows Forensics, Memory Forensics, Digital Forensics, RAM Analysis, Cyber Investigation, Incident Response, Mobile Forensics, Ransomware, Digital Evidence, and DFIR


เบอร์มือถือ : 089-960-5080
เบอร์บริษัท : 02-714-3801-3 ต่อ Hi-Tech Team
โทรสาร : 02-714-3804
อีเมล : 


Training Highlights | Digital Forensics – Unlocking the Secrets Training 02/09/2026
Training Highlights: Digital Forensics – Unlocking the Secrets
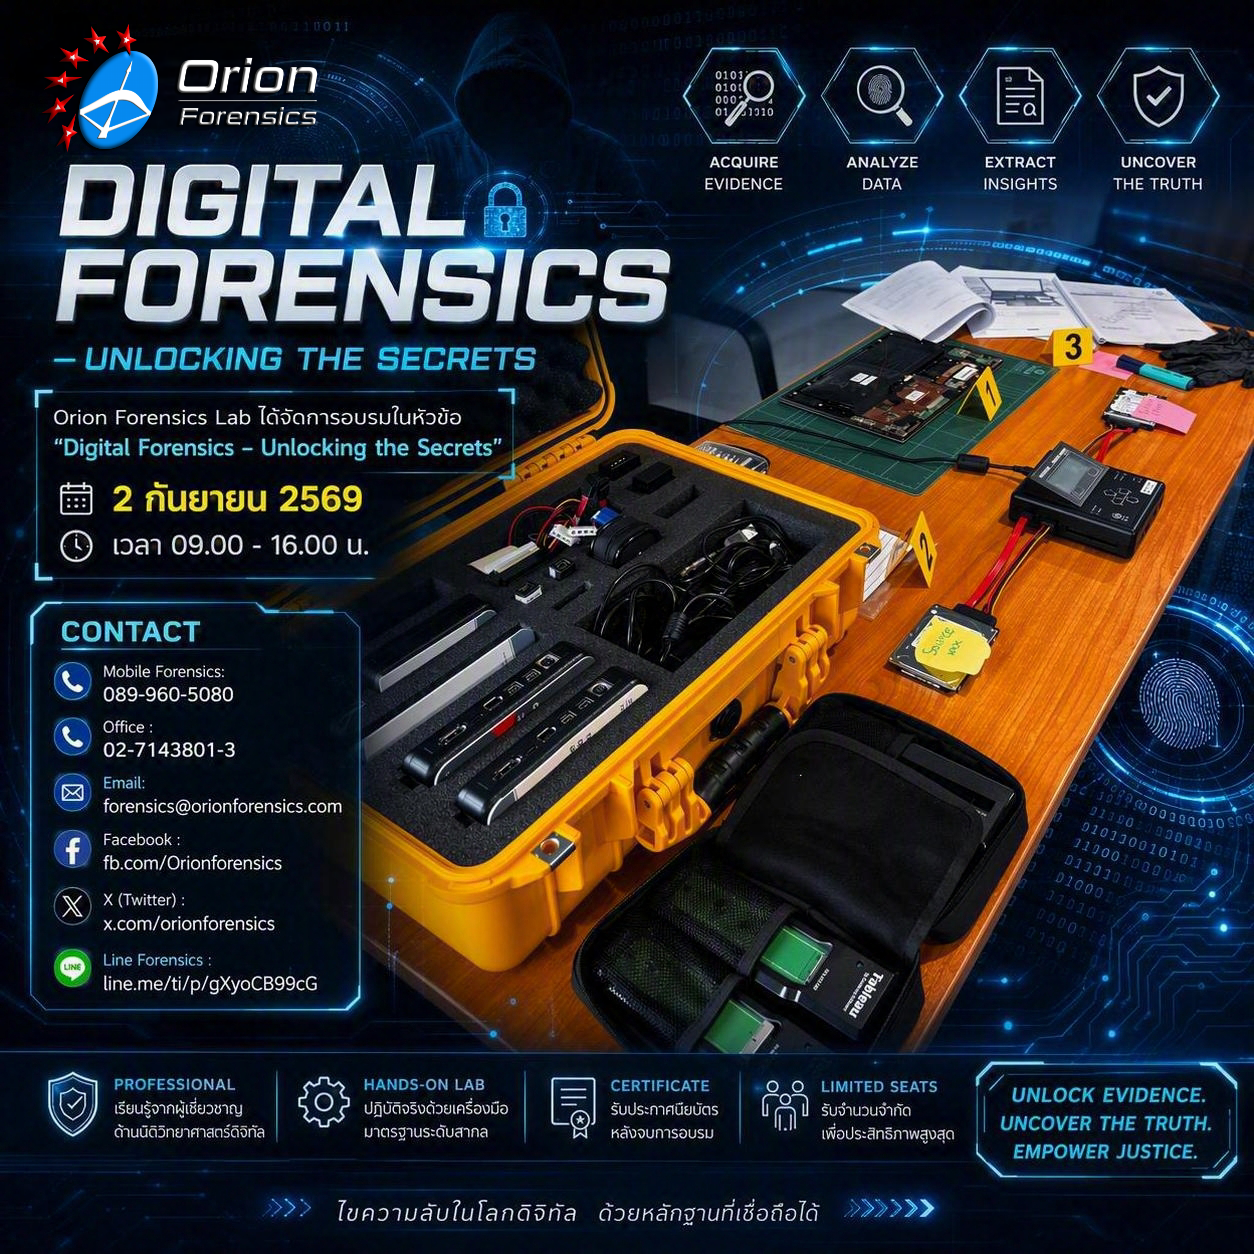
On September 2, 2026, Orion Forensics Lab conducted the training program Digital Forensics – Unlocking the Secrets at Orion Investigations Co., Ltd., Sukhumvit 63, Bangkok. The program was designed to enhance knowledge and practical skills in Digital Forensics for legal professionals and individuals interested in digital investigation processes.
Morning Session: Proper Preservation of Digital Evidence
Participants learned and observed demonstrations of a Forensic Duplicator, a critical tool used to preserve the integrity of digital evidence. The session also included demonstrations of data acquisition techniques from NVMe SSD storage devices in accordance with digital forensic standards, ensuring that acquired data can be properly presented as evidence in legal proceedings.
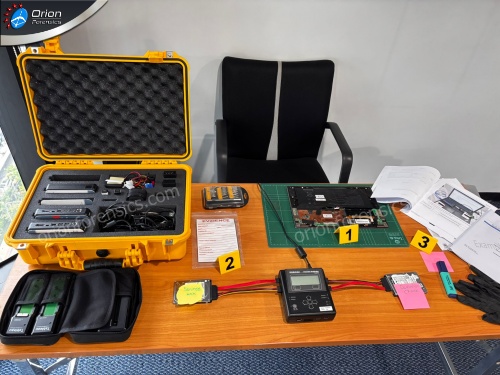
Afternoon Session: Mobile Forensics and Mobile Device Data Acquisition
During the afternoon session, participants learned techniques and procedures for acquiring data from mobile phones and portable devices through Mobile Forensics. Demonstrations included the use of specialized tools for Mobile Forensics Data Acquisition as well as supporting equipment commonly used in digital forensic investigations.
- Faraday Bags
- Connection & Acquisition Tools
- SIM Card Readers and Adapters
- Protective Gloves and Precision Screwdriver Kits
- Chain of Custody Documentation Forms
- Sample Digital Forensic Examination Reports
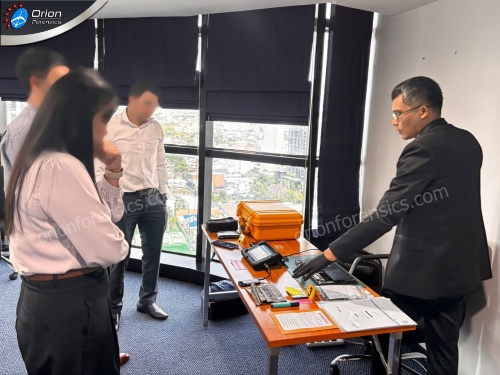
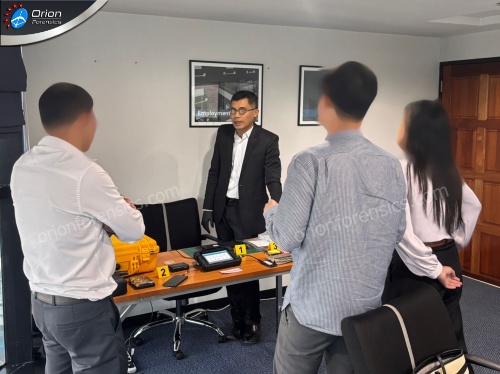
Enhancing Knowledge of Digital Evidence
This training program focused on providing participants with a comprehensive understanding of the principles, procedures, and best practices for collecting, analyzing, and preserving digital evidence from various devices, including smartphones, tablets, and electronic storage media. The goal was to ensure that information could be properly utilized as Digital Evidence in accordance with both legal and technical standards.
In addition, participants exchanged experiences with Digital Forensics professionals and attendees from the legal sector. Lawyers shared practical insights into courtroom proceedings, online evidence collection, and the use of GPS Data, IP Addresses, Metadata, and Event Logs. Discussions also covered website fraud investigations and the use of Social Media Evidence within the justice system.
Thank You to All Participants
Orion Forensics Lab would like to express its sincere appreciation to all participants for their interest and active participation throughout the training program. We hope that the knowledge, techniques, and experience gained during this course will be effectively applied in digital investigations, litigation support, and the management of digital evidence in accordance with international best practices.
Orion Forensics Lab – Unlocking the Secrets of Digital Evidence 🔍📱💻⚖️
Mobile : 089-960-5080
Office : 02-714-3801-3 to Hi-Tech Team
Fax : 02-714-3804
Email :